Healthcare’s Tracking Pixel Problem Just Got Expensive
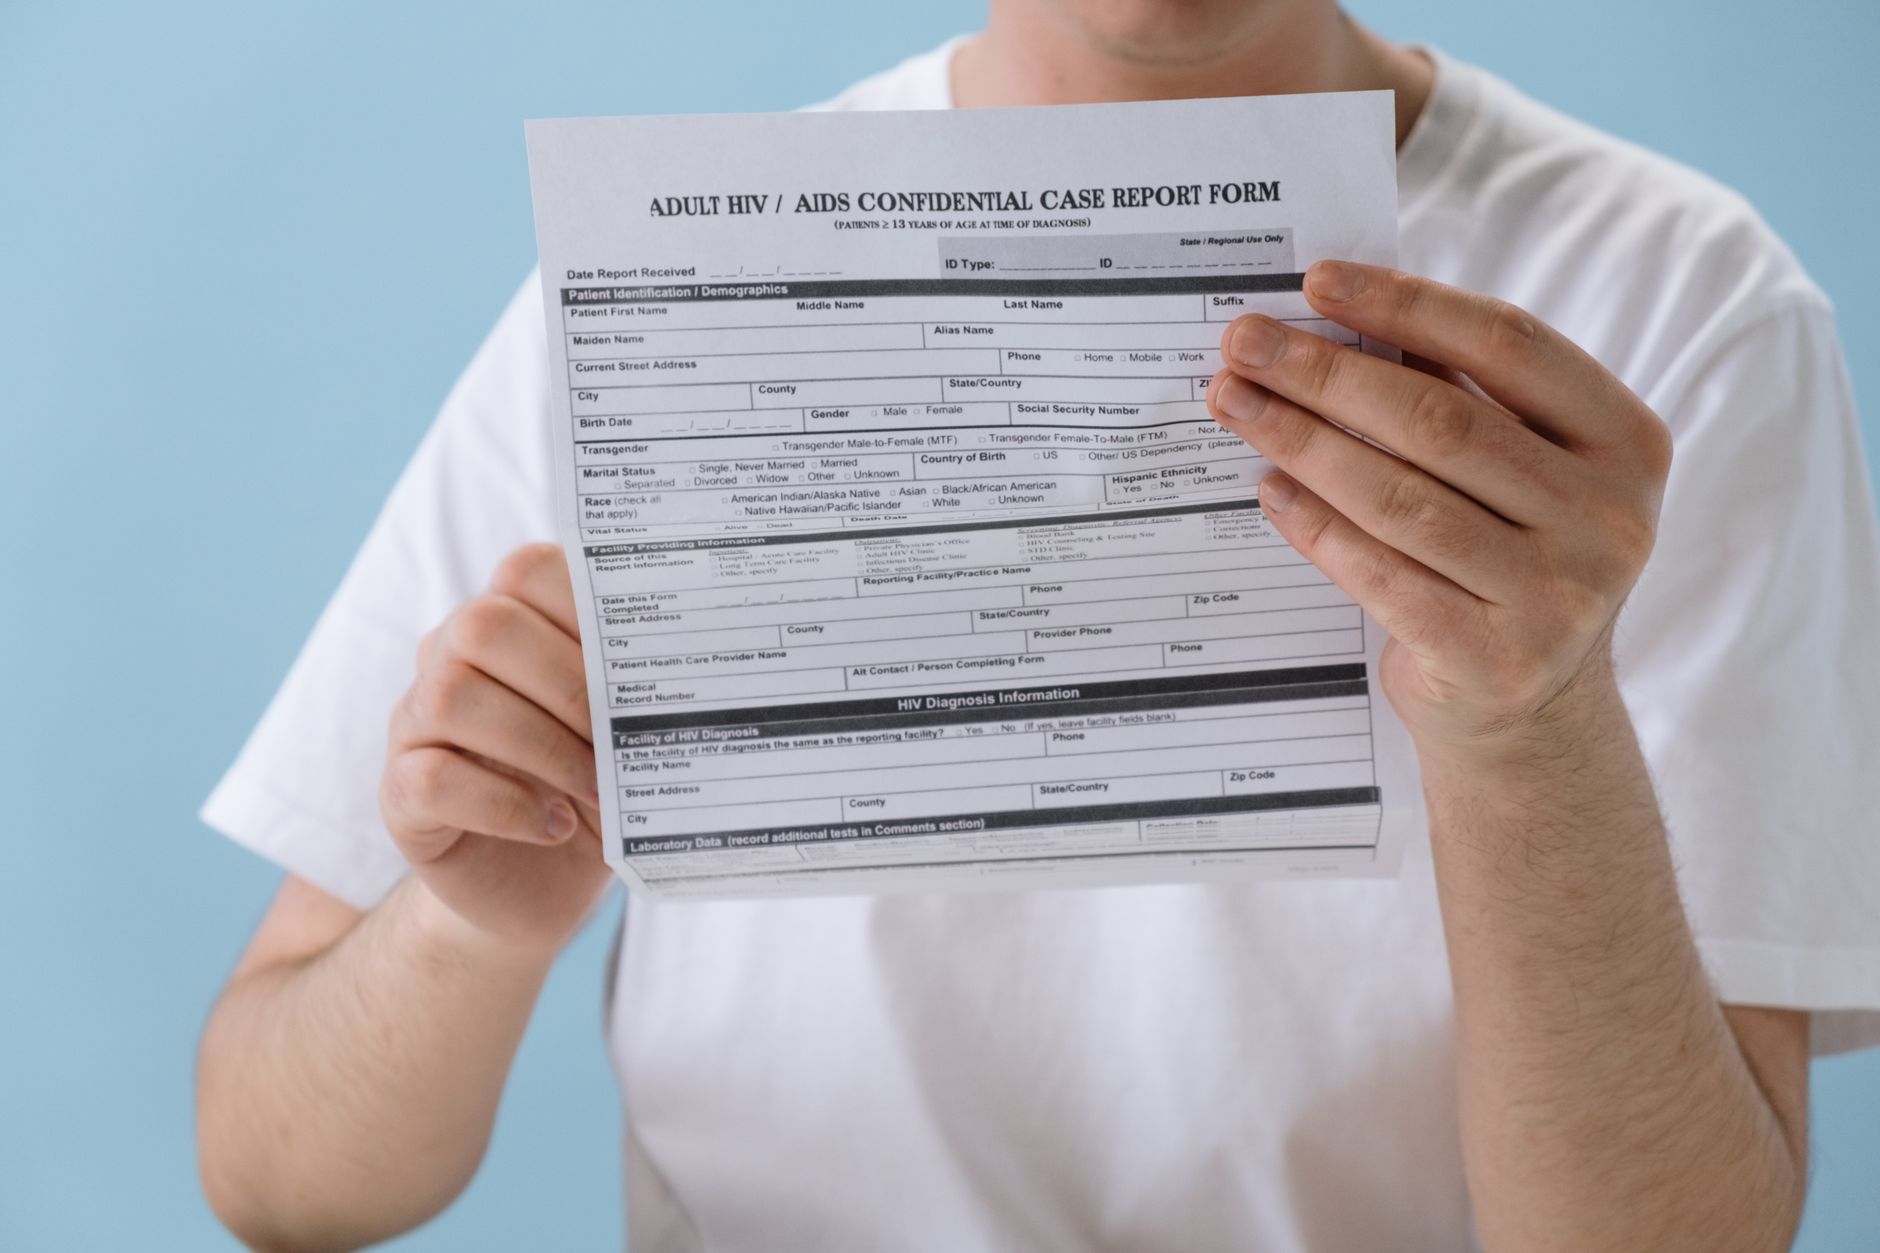
Two major health systems just paid up. Banner Health and LifeStance Health Group both settled lawsuits alleging they let tracking pixels — those invisible snippets of code from Meta, Google, and a dozen other ad tech vendors — hoover up patient data from appointment scheduling pages, symptom checkers, and portal logins. The settlements aren’t public dollar amounts, but the message is: plugging a Facebook pixel into a patient portal is a liability, not a marketing strategy.
The Pixels Were Never Anonymous
Marketing teams love the pitch: “Just drop this one line of code and we’ll optimize your ad spend.” What they don’t say is that the pixel fires on every page load, grabbing URL paths, button clicks, form field names, and often the hashed — but reversible — email or MRN sitting in the data layer. On a “Find a Doctor” page, that URL might read /cardiology/dr-smith?patient_id=12345. The pixel owner now knows someone in that household is shopping for a cardiologist. HIPAA calls that PHI. The plaintiffs’ bar calls it a class action.
Banner Health, a 30-hospital system based in Arizona, and LifeStance, a behavioral health network operating across multiple states, both had pixels on authenticated patient portal pages. Not just the public marketing site. The portal. Where patients message providers, view lab results, and pay bills. That distinction matters. Courts have consistently ruled that once a user logs in, the expectation of privacy is absolute. The Meta Pixel litigation in the Northern District of California established that precedent last year; these settlements show health systems are reading the tea leaves.
Consent Banners Don’t Fix This
Some compliance officers think a cookie banner solves it. It doesn’t. HIPAA doesn’t recognize “legitimate interest” as a lawful basis for disclosure. You need a Business Associate Agreement with every vendor receiving PHI. Google Analytics doesn’t sign BAAs for its free tier. Meta doesn’t sign BAAs for the Conversions API. The only compliant path is either (a) strip the pixels off authenticated pages entirely, or (b) route every event through a first-party collector you control — then push only de-identified, aggregated data to marketing tools under a BAA. Most health systems lack the engineering bandwidth for option (b). So option (a) becomes the default.
I’ve watched three hospital CIOs scramble in the last quarter to audit every script loading on their MyChart or Epic MyChart instances. They find 12 to 40 third-party requests on the login page alone. Hotjar. FullStory. Amplitude. A TikTok pixel someone’s intern added for a campaign that ended in 2021. Each one is a potential disclosure. Each one needs a BAA or a kill switch.
The Vendor Contract Gap
Here’s the part nobody discusses at HIMSS: your EHR vendor’s contract probably indemnifies them for third-party scripts you authorize. Epic’s standard language says the customer owns the “content and configuration” of the portal. Cerner’s says similar. So when the plaintiff’s attorney subpoenas the pixel payload logs, the health system stands alone. The marketing agency that recommended the pixel? They’re not a business associate. The ad platform? They claim they’re a mere conduit. The health system ate the risk for a 3% lift in appointment conversions.
Banner and LifeStance likely settled because discovery would have exposed pixel payloads containing MRNs, ICD-10 codes, and medication names in query strings. That’s not speculation — the Meta Pixel discovery produced exactly those logs. The judges didn’t buy the “hashed identifier” defense. SHA-256 an email with a known salt and you’ve just pseudonymized, not anonymized. HIPAA’s expert determination method requires genuine statistical de-identification. Marketing pixels don’t do that.
What a Real Audit Looks Like
If you’re a privacy officer reading this, here’s your Monday checklist:
- Pull the HAR file from your portal’s login, dashboard, and messaging pages. Count every third-party domain.
- Map each domain to a vendor contract. Flag any without a BAA.
- Inspect the payload. Look for URL parameters, data-layer pushes, or localStorage reads that contain patient identifiers.
- Kill the script. Replace with a server-side event stream you control.
- Document the removal. Date-stamp the commit. That’s your evidence when the demand letter arrives.
It takes a sprint. Two if your tag manager is a mess. But it’s cheaper than a settlement — and cheaper than the Wall Street Journal headline that follows.
Marketing Will Scream. Let Them.
Your CMO will argue you’re killing attribution. They’re right — you’re killing their attribution model. Build them a clean alternative: a first-party event bus that emits “appointment_scheduled” with a synthetic session ID, no PHI, pushed to your CDP. The CDP enriches with campaign metadata stored in a first-party cookie. Marketing gets their funnel. Legal gets sleep. Patients get privacy. The only loser is the ad tech vendor who lost a free ride on your patient traffic.
Banner and LifeStance just learned that lesson the expensive way. Everyone else gets to learn it the cheap way — if they move this week.
Source: original report